Your Cookie Banner Doesn’t Cover Your Integrations: How GA4 Ad Platform Links Can Bypass User Consent
Every privacy conversation I have with a platform rep eventually arrives at the same place. They want more data, they have a technically simple way to get it, and the legal risk of getting it that way sits entirely with us and with our clients. The pitch is always framed as a benefit: link these two accounts, see a few more conversions, optimize better.
The specific version of this I want to walk through is the property-level integration. GA4 to Google Ads. GA4 to Meta. These take only a few clicks to enable. They route data at a layer your cookie banner was never built to reach.
If you work in MedTech, healthcare, or any other privacy-first industry, that gap is the kind of exposure regulators and plaintiffs’ attorneys can seize on.
What Cookie Consent Actually Governs: Use, Not Just Collection
Start with what a user thinks they are doing when they interact with your banner. When someone accepts performance cookies and denies advertising cookies, they are not making a narrow statement about which scripts fire in the next 200 milliseconds. They are expressing a preference about use: “You may measure my behavior, and you may not use my data to advertise to me.”
That is the plain-language reading, and European law broadly agrees with it. ePrivacy governs storing and reading data on a user’s device. GDPR’s purpose limitation principle governs what happens after that: data collected for one purpose can’t simply be repurposed for another the user never agreed to. Consent to measurement is not consent to advertising.
US law gets to a similar place by a different road. California’s CPRA (CCPA) gives consumers the right to opt out of “sharing,” meaning disclosing personal information for cross-context behavioral advertising. A pipe that carries click IDs from your analytics into an ad platform looks a lot like sharing.
Where Consent Is Actually Enforced: The Collection Layer (Using GTM Tags as an example)
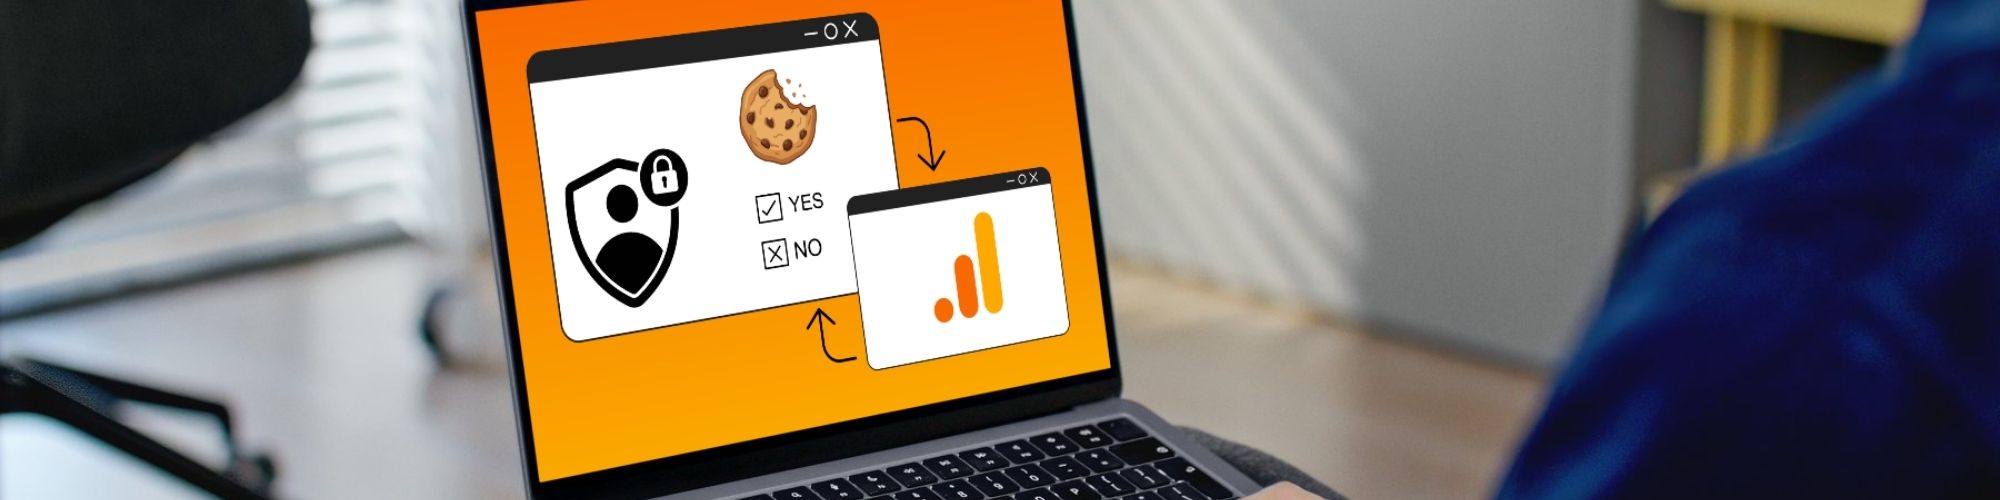
Now look at where the enforcement mechanism lives. A consent management platform (CMP) records the user’s choice by category and decides which tags and scripts are allowed to run. For most vendors, that is the whole mechanism: a denial of targeting cookies blocks every targeting tag, and nothing in that category fires.
Google adds its own layer on top, called Consent Mode. It passes the user’s choice to Google’s tags as signals for ad storage, ad user data, ad personalization, and analytics storage. It comes in two versions:
- Basic Consent Mode is a hard block. Google’s tags don’t load until the user interacts with the banner. If the user declines, nothing is sent to Google at all, not even the fact that they declined.
- Advanced Consent Mode loads Google’s tags immediately. While consent is denied, the tags still send “cookieless pings,” which Google uses to model the conversions and behavior it can’t measure directly. Those pings aren’t empty. Google’s own documentation says they can include the user agent, screen resolution, and IP address, though Google says GA4 doesn’t store the IP. And even with ad storage denied, the full page URL is still collected, click IDs included.
Either way, all of it operates at the moment of collection. The consent choice decides what a tag does as it fires. The problem is that collection is only one of two places your data moves, and the argument that follows holds in either consent mode.
How GA4 Integrations Move Data at a Second Layer Your CMP Never Sees
A GA4 property-level integration is an admin-configured, server-to-server relationship that makes GA4 data available to an ad platform. For Google Ads, the link makes GA4 data available for conversions used in bidding and for remarketing audiences. It does not read your CMP’s category choice. It is blind to it. The CMP knows what the user selected; the integration never asks.
So you end up with two structurally separate layers:
- The collection layer, where consent is captured and enforced, and where a denial actually stops something from happening.
- The sharing layer, where the data is already collected and the only question is where it goes next. Nothing here reads the user’s actual choice. At most, one vendor reads its own proprietary signal, stamped at collection time.
Data that a user consented to under a performance banner can arrive, through the second layer, in a platform built to target. In most cases the platform does not document precisely how it will be used, and that vagueness is doing real work for them. By the time anyone asks, the data is collected, the consent is recorded, and use is effectively their call.
This is the whole argument, and it is why I do not think the problem is a misconfiguration. No consent structure at the sharing layer reads the user’s choice, so there is nothing there to configure correctly.
What Google’s Recent Change to GA4 and Google Ads Data Sharing Admits
Google’s own behavior is the best evidence that this layer is being bypassed. Until June 15, 2026, two controls jointly governed whether Google Ads cookies and IDs were collected through GA4: the Google Signals setting inside GA4, and your Consent Mode settings. On that date, Google made Consent Mode the single control. Google Signals now governs only behavioral reporting inside GA4.
Google has said a second change is coming later in 2026: the ad_personalization signal will become the sole control over whether linked GA4 data is used for ads personalization, replacing the layered settings inside GA4. The stated goal is for Ads settings to “exclusively control Google Ads data (including data shared by Google Analytics).”
That is a reasonable principle, and I read the change as an admission. Google is conceding that the routing decision needed its own gate, separate from the collection-layer controls. It is also a partial fix at best, for four reasons:
- It requires Consent Mode v2 to be implemented, enabled, and correctly mapped to your CMP’s categories, plus configuration inside the ad platform.
- Outside Europe, gating is not enforced. Google’s own help center says that if you take no action, only users outside the EEA are included in audiences used by your linked ad products. For a US advertiser sending no consent signals, every user is in the shared audience.
- The gate at the destination still reads a signal stamped at collection time. Google Ads has no way to verify that the signal reflects what the user actually chose. More on that below.
- It is Google enforcing Google. It does nothing for any other platform you connect. And while Google says linked data becomes subject to Google Ads terms once it arrives, whether the consent behind that data was real is still your problem.
Why the Meta and GA4 Integration Is Harder to Defend
Meta’s version of this integration is configured from inside Meta. You accept Meta’s terms in Events Manager, sign into your GA4 account from their platform, and map GA4 events to a Meta dataset. Then data starts flowing. The one scoping control on offer is whether Meta can access “All traffic sources” or “Only traffic coming from Meta.”
Don’t confuse this with Google’s Meta Ads Data Import, which pulls Meta campaign metrics like cost, clicks, and impressions into GA4. That feature runs in the opposite direction, and it isn’t what this article is about.
There is no thorough technical documentation of what the integration collects or how it is used. The framing is that it is performance data used to help optimize campaigns, and that no PII is involved. Optimization is a flexible word. Getting better at targeting is optimization.
Meta does not document exactly what it pulls. But the access you grant at setup would let it query GA4 reporting data the way any Data API client can: any combination of dimensions and metrics.
Those reports are nominally aggregated, but aggregation only protects anyone if the dimensions are coarse. GA4’s page location dimension holds the complete URL, query string included. URL parameters in a Meta-sourced session routinely carry a Facebook click ID, unique to a single click.
Meta’s own developer documentation classifies the click ID built from fbclid as a “customer information parameter,” the same category as email and phone number, and uses it for ads attribution and delivery optimization. Report on page location and every fbclid becomes its own row, so “aggregated” stops meaning anything.
Google Ads carries the equivalent in a GCLID. Google’s own consent mode documentation notes that even when ad storage is denied, the full page URL is still collected, ad-click parameters included.
Meta’s defenders will point out that GA4 condenses rows into “(other)” once a report hits its row limit. That only kicks in when a report runs out of room. On the low-volume, condition-specific pages typical of healthcare and MedTech sites, many reports never get there.
Note, too, what the “Only traffic coming from Meta” option actually does. It narrows sharing to exactly the sessions most likely to carry an fbclid. It shrinks the scope; it does not make the integration consent-aware.
So a user who declined targeting cookies can still have a targeting-grade identifier handed back to the platform, through a dimension the integration has access to. Most consent leaks we have found in our own audits arrived through a URL parameter, including the accidental kind: a search term field that captured an email address a user typed by mistake.
The Consent Framework Isn’t Wrong. It’s Incomplete.
I want to correct one framing I have seen. It is tempting to say the consent framework governs the wrong layer. It does not. It governs the right layer; it just needs to govern a second one. Google’s June change is the closest any platform has come, and all it does is move the reading of a collection-time signal to the destination, for one vendor. The gap is built into how these integrations work, not into how any one account was set up. Google and Meta are not two anecdotes. They are two instances of the same architecture.
In an ideal world, a user’s full consent status would be shared transparently and be visible on every platform the data touches. Each downstream system could then determine what it is allowed to receive, what it can pass along, and what it can use. That world doesn’t exist yet. Until it does, the only gate you can trust is the one you control.
What We Recommend to Privacy-First Advertisers
My recommendation is blunt: do not use the integrations. Not in MedTech, not in healthcare, not anywhere the scrutiny is already elevated. If you use them anyway, tighten collection so that GA4 only receives data from users who granted both performance and targeting consent. That fix has a cost. Anyone who accepts performance cookies but declines advertising drops out of your analytics entirely, so your reporting gets thinner and less representative of your actual audience.
Meta reps have told us the integration is worth roughly 5% more conversions. Google makes a similar pitch: its help center says linking GA4 and Google Ads is correlated with a 23% increase in conversions. Ask what those numbers measure, conversions the platform caused or conversions it now gets credit for, and whether that is worth the potential legal trouble.
For the common Google Ads use case, advertisers link GA4 so conversions flow through without anyone building tracking at the collection layer. Instead of the link, we recommend proper, consent-gated conversion tagging in Google Ads. It is more accurate, you get more control, and you can see exactly what is being collected. The integration is a shortcut around technical work that should be done properly anyway.